Founder Of The Week: Danny Jenkins
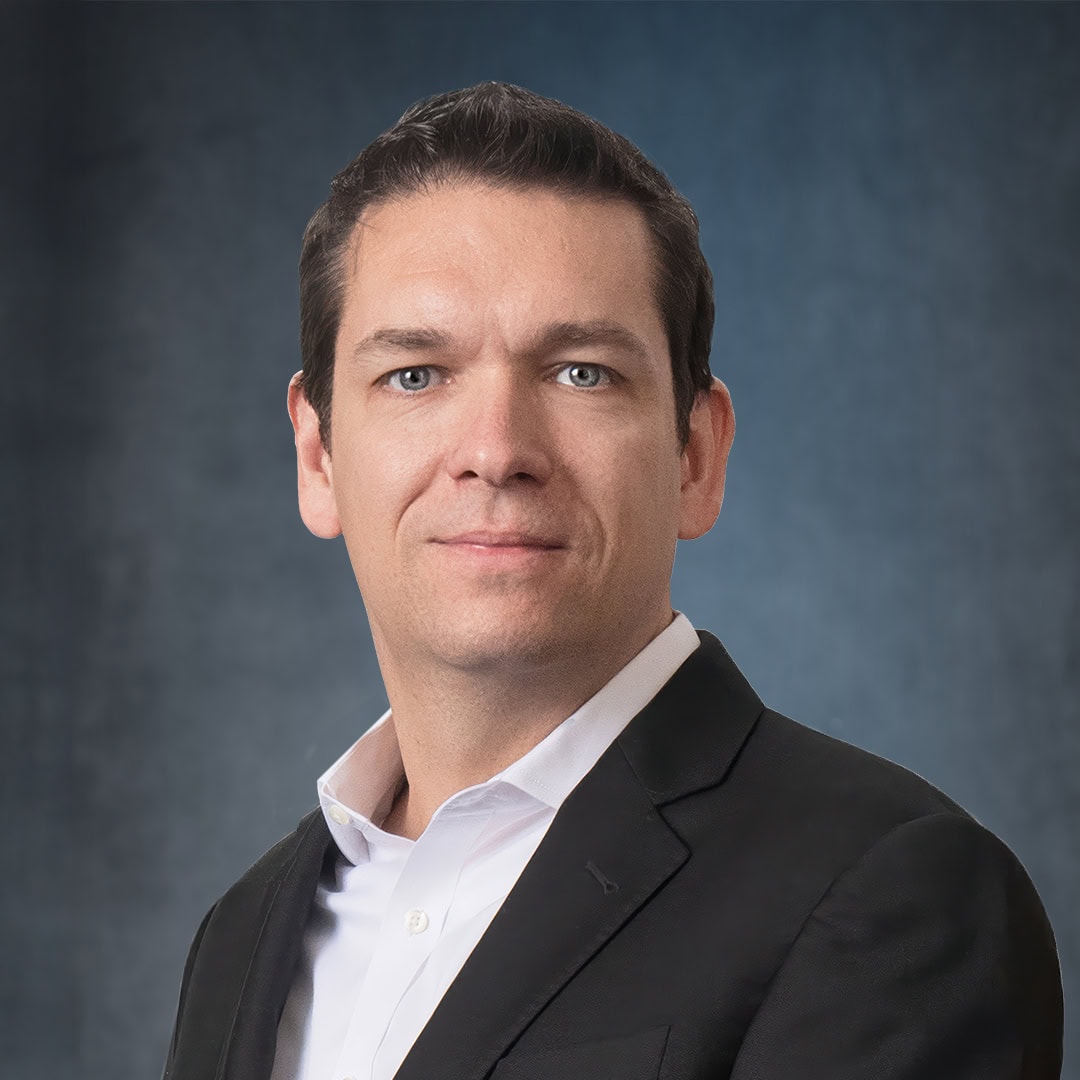
Tell Me About Yourself and ThreatLocker
I’ve been working with computers pretty much my entire life. I left school at 15 in the UK, got into IT, and eventually moved into ethical hacking and responding to cyberattacks. I spent a lot of time being called into companies after ransomware attacks, which is ultimately what led to ThreatLocker.
We started ThreatLocker in 2017 with a simple idea: instead of trying to identify everything that might be bad, we think businesses should decide what is allowed and deny everything else by default. Today, we have more than 600 people and protect more than 70,000 organizations around the world with our Zero Trust Platform.
What Inspired You To Start ThreatLocker, and What Problem Were You Trying To Solve?
I was responding to ransomware attack after ransomware attack, and I got frustrated because we kept having the same conversation. Someone would get attacked, everyone would clean it up, buy another security product, and then wait for the next attack.
At some point I thought, why are we continuing to ask whether something is malicious? Why don’t we decide what software should be able to run and what it should be allowed to do? The idea behind ThreatLocker was about making that model practical and scalable for businesses of all sizes. I wanted to prevent the attack rather than be the person showing up afterward to clean it up.
What Has Been Your Biggest Challenge So Far, and How Did You Overcome It?
Probably just surviving the beginning. In 2017, my wife Sami, our COO, and I were putting everything into the company. Our credit cards were getting close to their limits and then Hurricane Irma dropped a tree on our house.
There wasn’t really some brilliant strategy for getting through that period. You just kept moving and figured out what the next step was. In 2018, we landed a customer with about 110 endpoints that gave us enough breathing room to keep going, and shortly after that we started bringing in investment, and we were off to the races.
Can You Describe a Pivotal Moment That Significantly Shaped the Direction of ThreatLocker?
One of our early customers told us they needed 24-hour support. There were basically three of us in the company at the time, and I said, “Yes, of course we have 24-hour support.”
I installed speakers in the ceiling of my house so if a support request came in at two in the morning, it would wake me up. Eventually we changed the system so responses came from “Cyber Hero” rather than my name. That let me focus on solving the problem rather than explaining why the CEO was handling it. That became the Cyber Hero Team we have today. It taught us very early that if you’re selling cybersecurity, customers need to know somebody is going to be there when they need help. That became part of the culture of the company, not just a feature of the product.
For your business: I want to build something that actually changes the way cybersecurity is done. I’ve done well financially, and I’m obviously grateful for that, but that’s never been what gets me out of bed. I still spend a lot of my time thinking about the product, talking to customers and looking at what attackers are doing next. If I’m still excited about solving those problems and we’re building something that makes a real difference, I consider that success.
As a founder: For me, success isn’t a valuation or how much money we’ve raised. The reason we built ThreatLocker was because we were tired of seeing businesses devastated by cyberattacks. The mission of ThreatLocker was to address that problem by changing the paradigm of cybersecurity from allow-by-default to deny-by-default. Success is when we achieve that mission and make cybercrime much harder and less profitable. Obviously, we want to grow the company, but growth gives us the ability to protect more organizations. That’s what matters to me.
What Advice Would You Give To Someone Thinking About Launching Their Own Startup?
Make sure you’re solving a real problem that you understand, not just something that sounds like a good business idea. Then get in front of customers as quickly as you can. You learn a lot more from someone using your product than you do sitting in a room talking about what the product should be.
What’s Next for ThreatLocker? Any Exciting Developments We Should Watch Out For?
We’re still growing very quickly. We raised another $190 million this summer, and a big part of that investment is going into the platform, international expansion, and security around AI.
AI is particularly interesting because we’re moving into a world where AI agents aren’t just answering questions. They’re being given access to files, applications, cloud systems and other sensitive resources. From a security standpoint, you have to start treating those agents much like you would a user or an application. What exactly are they allowed to access, and what are they allowed to do? We need Zero Trust for AI.
Want to be featured as TechRound’s Founder of the Week? Find out more about this weekly feature and how to get involved here.
Founder’s 5 with Danny Jenkins
Want to know more about the man behind ThreatLocker? Here’s TechRound’s exclusive Founder’s Five with Danny Jenkins.
A stopwatch or timer app. They let me measure things like response and boot times.
Always maintain control of your business. It doesn’t necessarily mean you have to own 51% but make sure you keep control of the board.
Securing the internal AI systems businesses use.
“Never let the fear of striking out keep you from playing the game. – Babe Ruth
I still have the Window NT Networking Guide on my bookshelf, even though it’s outdated. I learned more from that book than any other resource in my career.
Want to be featured as TechRound’s Founder of the Week? Know someone who deserves to be recognised as a founder making waves in the startup landscape? Find out more about this weekly feature and how to get involved here.
Related Stories
 Cybersecurity
Cyber Security Authority (CSA) Ghana opens NCSAM 2026 with call for stronger cybersecurity collaboration
12 hours ago
 Cybersecurity
Information Technology hosts fair to raise cybersecurity awareness
5 days ago
 Cybersecurity
ShinyHunters hackers say they won't leak sensitive FBI data
6 days ago
 Cybersecurity
Dutch police arrest security professional in ShinyHunters investigation
1 week ago
 Cybersecurity
Tokyo rail firms report online security breaches
1 week ago
 Cybersecurity
What drives ShinyHunters, the group that claimed responsibility for hacking the FBI?
1 week ago
 Cybersecurity
Inside the FBI hack: Agents fearful and angry after 'dangerous' data breach
1 week ago
 Cybersecurity
ShinyHunters hackers say they breached FBI, stole employee data
1 week ago